

Table of contents of the article:
In a historic move, the European Union is preparing to adopt the first global legislation on cybersecurity. After intense negotiations, a few days ago (30 November), representatives of the European Parliament and the Council of the EU reached an agreement on the regulations proposed by the European Commission in September 2022.
These new rules will impose "proportionate and mandatory" cybersecurity requirements on all hardware and software products placed on the European single market. This spectrum includes a wide range of devices, from baby monitors to smartwatches, from computer games to firewalls and routers. Under the Cyber Resilience Act, IT manufacturers will be required to implement security measures throughout the product lifecycle, from design and development to market launch. Products deemed "safe" will receive the CE marking, a symbol of compliance with the Regulation's requirements and a guarantee of marketability throughout the EU.
The aim of this legislation is twofold: to ensure that digital products used on a daily basis meet high safety standards and to hold manufacturers accountable for the safety of their products.
According to Vera Jourová , European Commission Vice-President for Values and Transparency, 90% of products will require market participants to self-assess their cyber resilience. This category includes devices that run services such as photo editing, word processing, smart speakers, hard drives, and video game consoles. The remaining 10% will be divided into two criticality classes: "Class I," which includes password managers, network interfaces, and firewalls, will require predefined standards or third-party assessments; while "Class II," which includes operating systems and industrial firewalls, will require an independent assessment.
Thierry Breton, EU Commissioner for the Internal Market, emphasizes the crucial importance of cybersecurity not only for consumers, but for society as a whole. The number of cyberattacks on the software supply chain has tripled in the past year, with an estimated cost of approximately €20 billion. In 2021, approximately 10 million DDoS attacks were recorded globally.
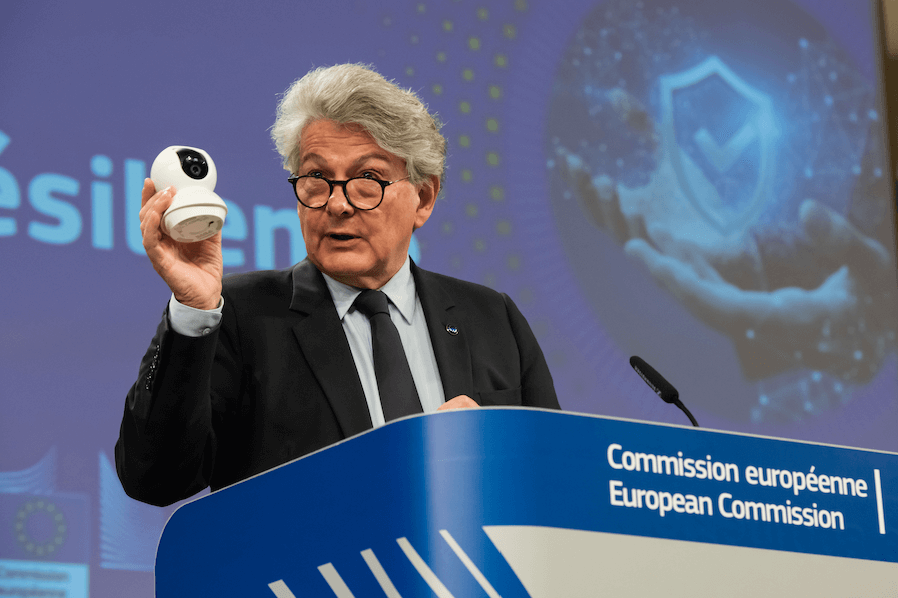
The final version of the law, shaped during interinstitutional trilogues, retained the general structure of the Commission's initial proposal. The legal obligation for manufacturers to provide security updates for a period of at least five years was confirmed. Furthermore, support measures for small and micro-enterprises, including awareness-raising and training activities, were included.
Before final adoption, the agreement must be ratified by the plenary session of the European Parliament and by the ministers of the 27 member states meeting in the Council. Once approved, the Cyber Resilience Act will be published in the Official Journal, and the new rules will enter into force three years later.
Cyber Resilience Act
The Cyber Resilience Act, a pioneering legislation in the field of cybersecurity, was proposed by the European Commission on 15 September 2022. This initiative is part of a broader commitment by the European Union to strengthen the resilience and security of its digital space . The regulation focuses on crucial aspects of cybersecurity for hardware and software products, aiming to raise and standardize security standards across the European single market.
Here are the key points of the Cyber Resilience Act:
- Security Requirements: It imposes the need to integrate robust cybersecurity measures into all phases of the product life cycle, from design to launch.
- CE marking: Products that meet the safety requirements will obtain the CE marking, indicating their compliance with EU safety standards and their suitability for sale throughout the Union.
- Evaluation and Compliance: It introduces a differentiated risk assessment system. While most products can be self-assessed for cyber resilience, some high-risk products require third-party assessments.
- Security Updates: It establishes an obligation for manufacturers to provide security updates for a minimum period of five years, ensuring protections against evolving cyber threats.
- Support for Small and Micro Businesses: It includes support measures for small and micro businesses, such as training and compliance assistance.
- Producers' Responsibilities: It accentuates the responsibility of manufacturers to ensure the safety of their products, encouraging the production of safer devices.
After its initial proposal in September 2022, the political agreement on the Cyber Resilience Act was reached on 30 November 2022 between negotiators of the European Parliament and the Council of the EU. This step represents a significant advance in the field of digital security, establishing rigorous standards for manufacturers and improving the protection of consumers and businesses against cyber threats. The implementation of this law marks a crucial moment for digital security in the European Union, aiming to create a more secure and resilient digital environment.

